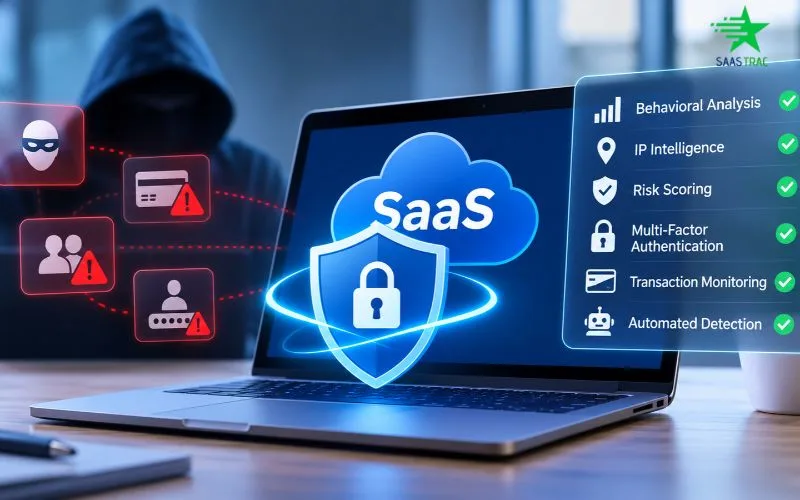
Users benefit from accessing subscriptions, registration, and service use from almost any location on a SaaS platform. That same flexibility, however, also makes these applications vulnerable to fraud.
Scams, identity theft, transaction fraud, and other criminal activities can easily cost a business money or create security vulnerabilities. SaaS businesses respond by incorporating continuous monitoring of user behavior and risk scores.
Why SaaS Platforms Are Attractive Fraud Targets
An average SaaS company may process hundreds or thousands of logins daily, including subscriptions, billing, and account creation and cancellation.
Many kinds of fraud can occur on a SaaS platform, including subscription fraud, fake account creation, credit card theft, account takeover, refund misuse, and chargeback scams. This is why modern fraud prevention tools use immediate fraud detection and risk assessment techniques, along with analysis, machine learning, and human judgment, to maximize protection and secure their assets.
How Modern SaaS Fraud Has Changed
Not every successful attack involves sophisticated malware or an unknown software vulnerability. Increasingly, attackers try to make malicious activity resemble legitimate customer behavior.
Recent cyberattacks have shown that threat actors target SaaS integrations, trusted access paths, authentication systems, compromised tokens, social engineering, and legitimate privileges and identities. The last ones, identity-based attacks, are especially difficult to distinguish from normal activity because attackers can use valid credentials and approved applications. That makes context imperative to fraud detection.
SaaS Companies Look for Multiple Risk Signals
Instead of automatically blocking every suspicious activity, fraud detection systems look for multiple signals to determine the overall risk of a specific session or transaction. Some common signals include:
- IP address and location
- Device and browser characteristics
- Unusual login attempts
- Payment and transaction patterns
- Account age and history
- Rapid changes to account information
- Behavioral anomalies
- Known compromised credentials
IP Data Adds Useful Context
IP address data can add useful context to the fraud detection puzzle. For instance, a strange IP address from a location that the user doesn’t typically log in from may prompt additional verification, especially if other unusual activity is connected to the login.
Teams can use an IP lookup tool to check basic information associated with the address. However, IP information should be only one signal among many, since real users can travel or use VPNs and other services that rotate their visible IP addresses.
Behavioral Analysis Helps Detect What Rules Miss
Static fraud rules are still useful. A SaaS company can identify multiple failed login attempts, an unusually high transaction value, or multiple accounts using the same payment details.
Behavioral analysis adds a layer of security by asking whether the activity is appropriate for that particular user.
A customer who usually logs in from one device but suddenly logs in from a different device and immediately changes the billing information may require extra attention. By comparing what the customer is doing now with the customer’s past habits, SaaS companies can spot unusual actions even if every single one looks technically correct.
Risk Scoring Enables Real-Time Decisions
Today’s fraud detection systems can translate those signals into a risk score. Rather than treating all suspicious activity the same way, the system calculates the probability that an incident is fraudulent.
Low-risk sessions can proceed as normal. Medium-risk incidents could trigger a higher level of authentication, while high-risk incidents could be prevented or require further review.
Another benefit of this strategy for SaaS companies is its ability to prevent fraud without inconveniencing legitimate clients.
Account Takeover Requires Layered Protection
Account takeover is particularly dangerous because an attacker uses a valid user’s account. Attackers can take over accounts through stolen credentials, phishing, credential stuffing, or compromised sessions. For instance, in credential stuffing, attackers use lists of usernames and passwords stolen from other sites to log into other accounts.
Strong Authentication Limits the Damage
If passwords are hacked, multi-factor authentication (MFA) can help. MFA adds protection when credentials are compromised, while risk-based authentication determines when suspicious sign-ins should face another round of verification.
After someone logs into their account, session monitoring is just as important. If the account suddenly starts downloading large volumes of data, changes user permissions, creates new administrators, or accesses resources that are not commonly used, this could indicate that the session has been taken over. Quick detection of unusual behavior helps SaaS companies prevent further damage.
Payment Fraud Needs Its Own Detection Layer
For subscription-based companies, the risk isn’t limited to the login screen. Malicious actors may use compromised credentials to exploit free trials and buy something they will return or refund, or buy something using stolen payment cards. Payment monitoring can compare account behavior with past activity, while velocity checks can detect failed login attempts that may indicate fraudulent activity.
The goal is not simply to reject more transactions or block more accounts. Effective systems distinguish risky behavior while allowing legitimate customers to complete purchases with minimal interruption.
Automation Helps SaaS Companies Respond Faster
Manual detection is impractical as activity on SaaS platforms continues to grow. This is where automated systems step in and can help by monitoring logins, account changes, transactions, and other events to report based on their risk levels.
Machine learning can detect evolving trends that pre-set rules may miss. However, it’s also important to have human expertise to review activity that is ambiguous or could have a high impact on the company.
Combining automated detection with human review is often the strongest approach, especially when additional context is required.
Building SaaS Growth on Trusted Access
Contextual awareness is what drives current fraud prevention efforts within SaaS companies. IP data, devices, sign-ins, payments, authentication factors, risk scores, and more all become more valuable when viewed as a whole.
Through continuous monitoring, multilayered authentication, automation, and analysis, SaaS organizations can react quickly to threats while maintaining ease of access. This balance is crucial to protecting customers, sales, and the company’s reputation.